UFW Firewall Rules: Practical Examples for Securing Your VPS
Your VPS is online 24 hours a day, which means it is also reachable by anyone who knows its IP address. This guide shows you how to set up UFW firewall rules on a VPS, with practical examples you can copy and adapt.
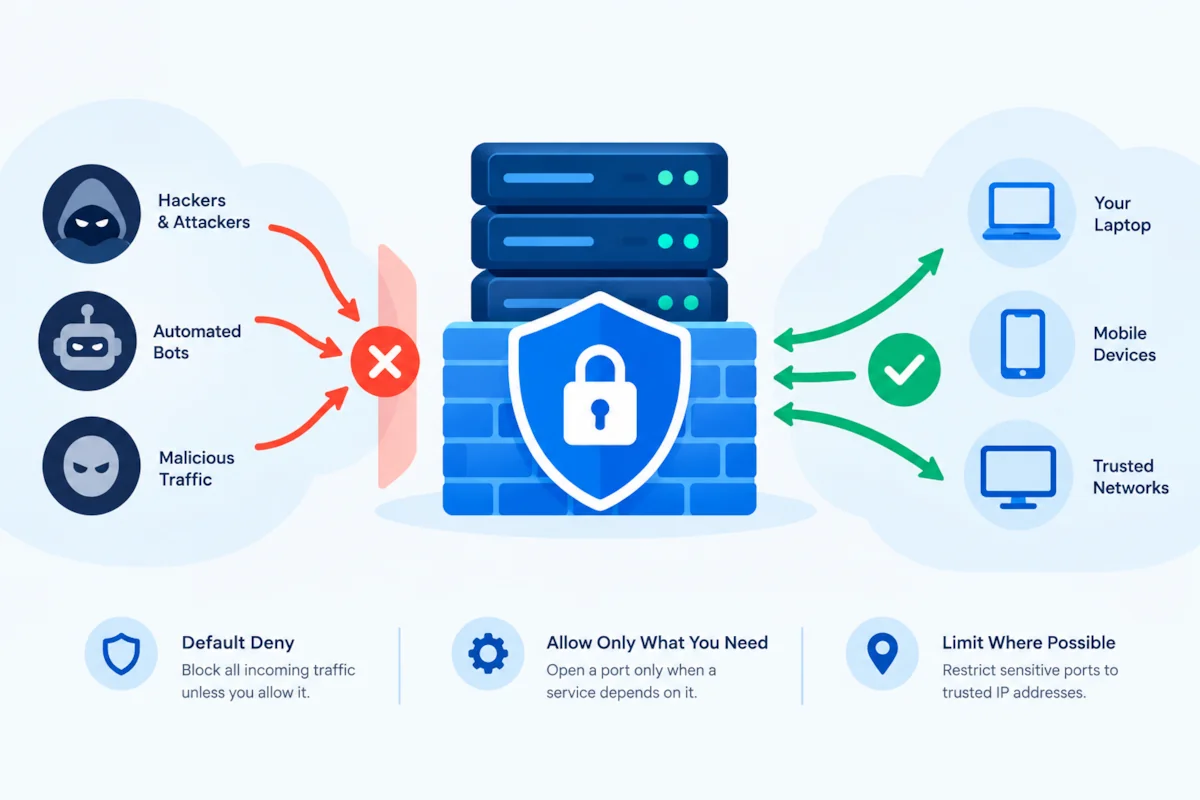
Your VPS is online 24 hours a day. That means it is also reachable 24 hours a day, by anyone who knows its IP address. Automated bots scan the internet constantly, looking for open ports, weak logins, and services they can exploit.
A firewall is your first line of defense. It decides which traffic may reach your server and which traffic gets blocked. On Ubuntu and Debian, the simplest way to manage a firewall is UFW, short for Uncomplicated Firewall.
This guide shows you how to set up UFW firewall rules on a VPS, with practical examples you can copy and adapt. You don’t need to be a network expert. You need a clear plan and a few careful steps.
What UFW Does
UFW is a front end for iptables, the Linux packet filter built into the kernel. Instead of writing long, complex firewall chains, you write short commands like ufw allow 80/tcp. UFW turns them into the right low-level rules.
Three ideas drive a good UFW setup:
- Default deny: Block all incoming traffic unless you explicitly allow it.
- Allow only what you need: Open a port only when a service depends on it.
- Limit where possible: Restrict sensitive ports to trusted IP addresses.
When you follow these three rules, most automated attacks never reach your applications.
Step 1: Install UFW and Set a Default-Deny Baseline
Check whether UFW is already installed:
sudo ufw status
If it is missing, install it:
sudo apt update
sudo apt install ufw
Now set the default policies. Deny incoming traffic, allow outgoing traffic:
sudo ufw default deny incoming
sudo ufw default allow outgoing
These two commands do not turn the firewall on yet. They only set the rules that will apply once it is running.
Step 2: Allow SSH Before You Enable the Firewall
This step matters more than any other. If you enable UFW without allowing SSH, you can lock yourself out of your server. Your current session may keep working, but the next login will fail.
Allow SSH first:
sudo ufw allow OpenSSH
If your SSH server runs on a custom port, such as 2222, allow that port instead:
sudo ufw allow 2222/tcp
Confirm the rule exists before you continue:
sudo ufw show added
Keep your current SSH session open while you test. Open a second terminal and confirm you can still log in.
Step 3: Allow Web Traffic
If your VPS hosts a website, open the standard web ports:
sudo ufw allow 'Nginx Full'
This opens both port 80 (HTTP) and port 443 (HTTPS). On Apache, use sudo ufw allow 'Apache Full'. If you only need plain HTTPS, you can open just the one port:
sudo ufw allow 443/tcp
Avoid opening ports you don’t use. Every open port is a door someone can try.
Step 4: Enable the Firewall
Turn UFW on:
sudo ufw enable
UFW will warn you that existing SSH connections may drop. Type y to confirm. Then check the status:
sudo ufw status verbose
You should see your default policies and your allowed rules listed. Test a new SSH login from another terminal before you close anything.
Step 5: Restrict Access to Trusted IP Addresses
Some services should never be open to the whole internet. A database port is a good example. Allow it only from your application server or office network:
sudo ufw allow from 203.0.113.25 to any port 3306 proto tcp
Replace 203.0.113.25 with the trusted IP address. This rule lets that one address reach MySQL on port 3306. Everyone else stays blocked.
You can also limit SSH to your own IP:
sudo ufw allow from 203.0.113.10 to any port 22 proto tcp
Use this only if your IP address is stable. If it changes often, your own access could be blocked. Keep your hosting provider’s web console handy as a backup.
Step 6: Protect SSH From Brute-Force Attempts
UFW can slow down repeated login attempts. The limit rule allows a connection but blocks an IP address that opens too many connections in a short time:
sudo ufw limit OpenSSH
Rate limiting is a useful layer. For stronger protection, pair it with key-based login and a tool like Fail2Ban.
Step 7: Block a Specific IP Address
If you see an address that keeps probing your server, block it:
sudo ufw deny from 198.51.100.44
To block an entire range, use CIDR notation:
sudo ufw deny from 198.51.100.0/24
Be careful with broad ranges. You can lock out legitimate users if you block too much.
Step 8: Manage and Remove Rules
List your rules with numbers:
sudo ufw status numbered
Delete a rule by its number:
sudo ufw delete 4
Or delete a rule by specifying it the same way you added it:
sudo ufw delete allow 443/tcp
Numbered rules make cleanup easier, but always check the list again before deleting. Rule numbers change after each deletion.
Step 9: Turn On Logging
Logs show what UFW blocks. They help you spot patterns and confirm your rules work:
sudo ufw logging on
View recent entries:
sudo tail -n 50 /var/log/ufw.log
Look for repeated BLOCK messages from the same source. Those are often scans or attack attempts. Logging adds some disk use, so review your log size over time.
Step 10: Check IPv6 Settings
UFW can manage IPv6 as well as IPv4. Make sure IPv6 support is on in /etc/default/ufw:
IPV6=yes
If you enable IPv6 and forget about it, a service may be reachable over IPv6 even though you blocked it over IPv4. Check both protocols when you test your rules.
A Note on Docker
Docker writes its own iptables rules. Published container ports can bypass UFW rules, even when UFW shows them as blocked. If you run containers, check your exposed ports with sudo ss -tulpn and review your Docker port mappings. Binding containers to 127.0.0.1 and placing a reverse proxy in front of them is a safer pattern.
Quick Checklist
Before you finish, confirm the following:
- Default policy is deny incoming.
- SSH is allowed and tested in a second session.
- Only required web or application ports are open.
- Sensitive services are limited to trusted IP addresses.
- Logging is on, and you know where to find the log.
- IPv6 rules match your IPv4 rules.
Hostzop Cloud: Secure Your VPS With Confidence
Setting up UFW firewall rules correctly takes care, and a single mistake can cut off access to your own server. Hostzop Cloud gives Indian businesses VPS Hosting In India built with a security-first approach, so you start from a protected baseline and extend it as your needs grow. Our platform supports standard Linux distributions and clear documentation for common tasks like firewall configuration, port management, and SSH access control. With responsive support and transparent INR pricing, Hostzop Cloud helps startups and SMBs secure their cloud server without the overhead of a full security team.
Frequently Asked Questions
Is UFW enough to secure a VPS?
UFW is a strong foundation, but it is one layer. Combine it with key-based SSH login, regular updates, Fail2Ban for repeated login attempts, and sensible application security.
Why does my site still work after I deny a port?
Check whether the service runs on a port you allowed, such as 80 or 443. Also check whether Docker is publishing the port, since Docker can bypass UFW rules.
How do I reset UFW to start over?
Run sudo ufw disable, then sudo ufw reset. Reset clears all rules, so add your SSH rule again before you re-enable the firewall.
What is the difference between allow and limit?
allow opens a port. limit opens a port but blocks an IP address that makes too many connection attempts in a short period. It is commonly used for SSH.
Can I allow a port only for one protocol?
Yes. Add /tcp or /udp to the rule, for example sudo ufw allow 53/udp.